
A poisoned HTML file could escape the Claude Code Desktop preview pane and read credentials from your disk. Noma Labs named the flaw SneakPeek; Anthropic scored it CVSS 8.7 (High). It is fixed in Claude Desktop 1.30096.1 and later through auto-update, so check that your app has updated, and read on for what was exposed.
| Question | Short answer |
|---|---|
| Am I affected? | If you used the Claude Code Desktop preview on untrusted repositories before the August 17, 2026 fix. The affected range was not published |
| Is there a fix? | Yes: Claude Desktop 1.30096.1 and later, delivered by auto-update |
| Does it need a click? | No extra prompt, per Noma: asking Claude to look at the file was enough |
| Is there a CVE? | Pending at publication |
| Does data leave my machine? | In the attack, yes: the script sent it to an attacker's server |
How the SneakPeek attack works
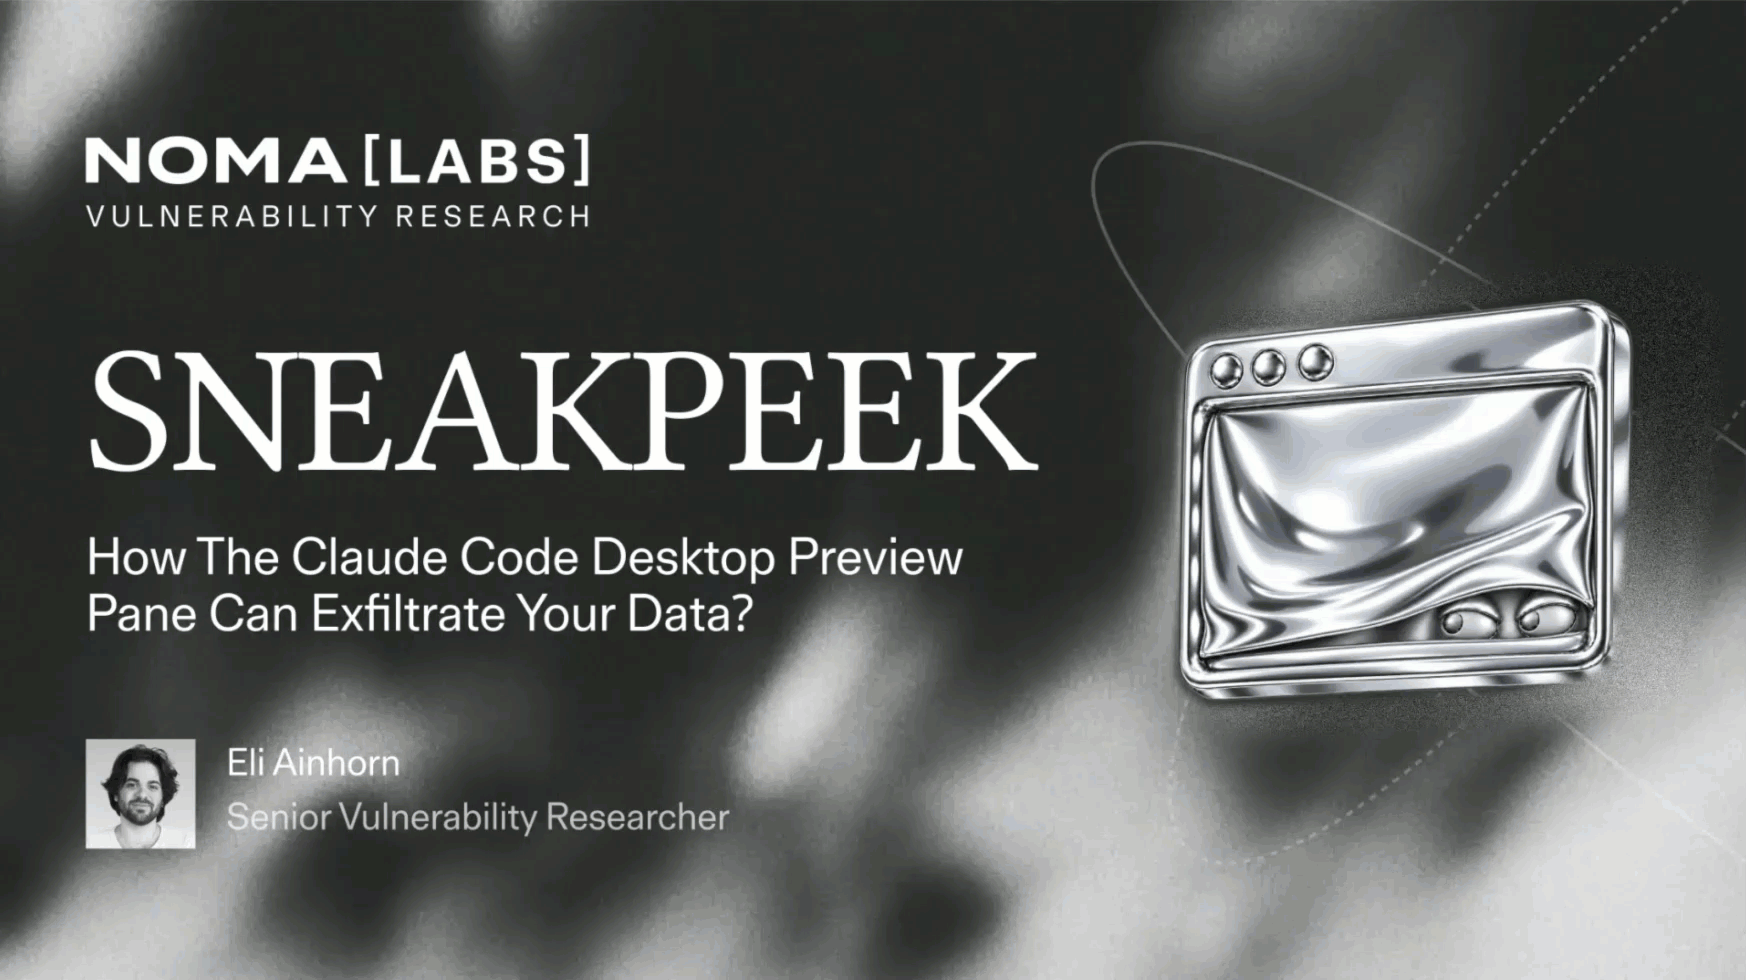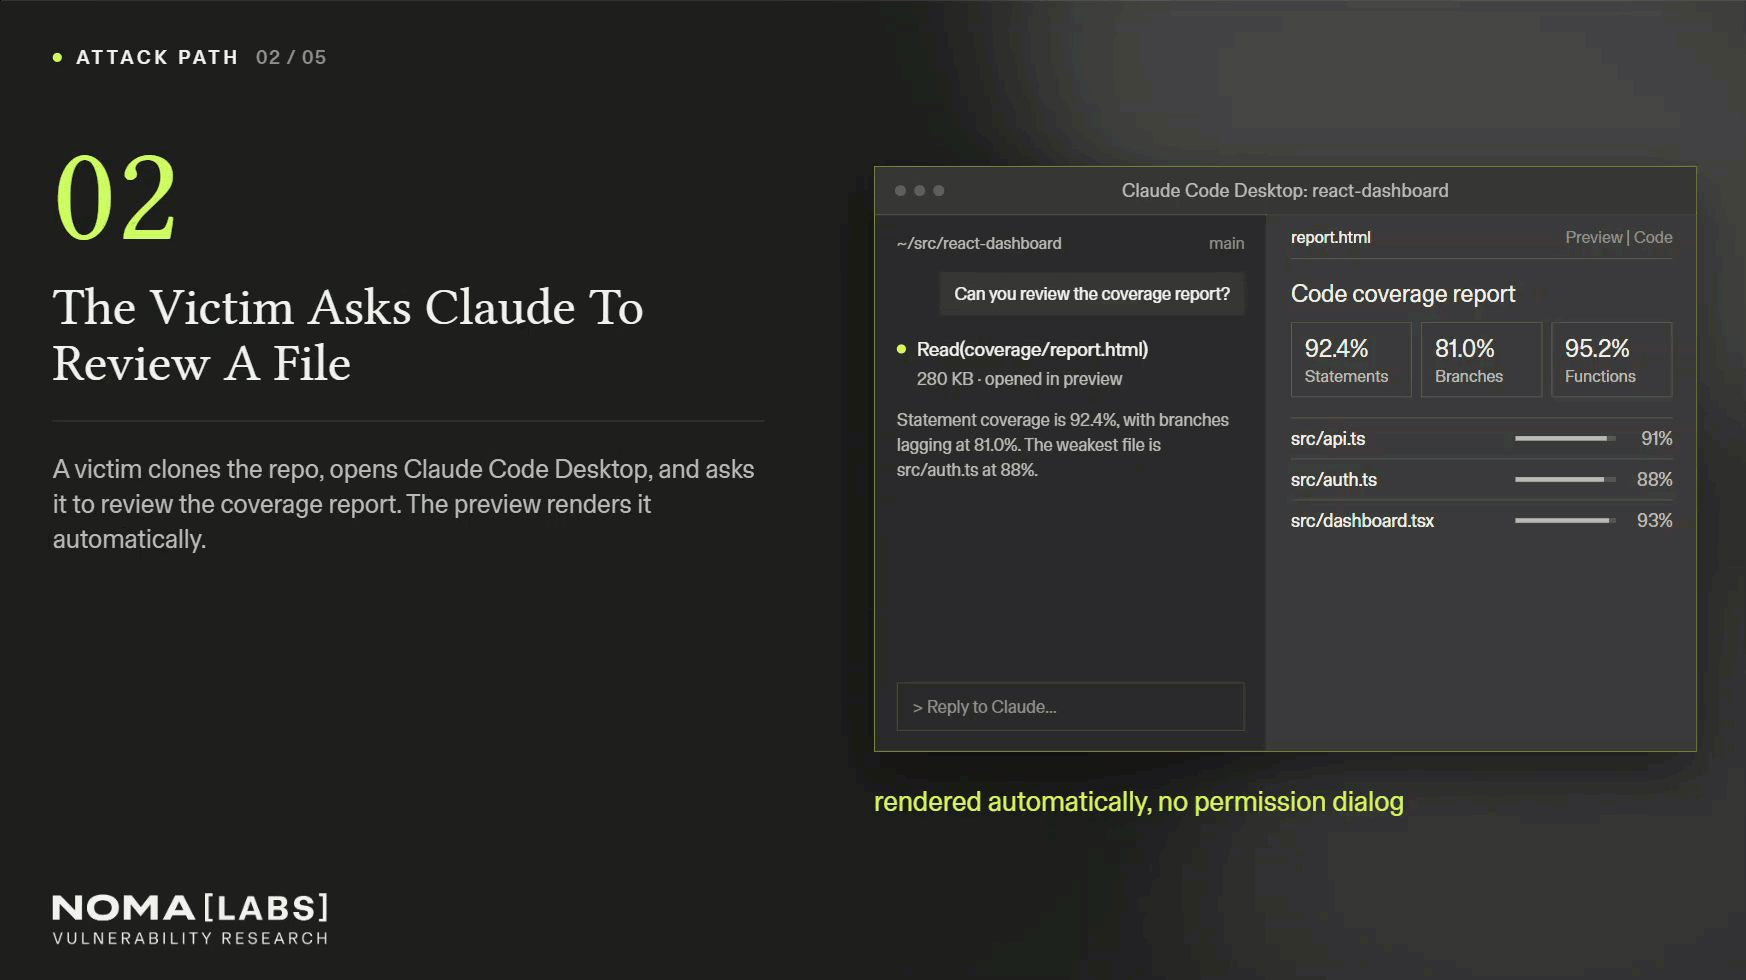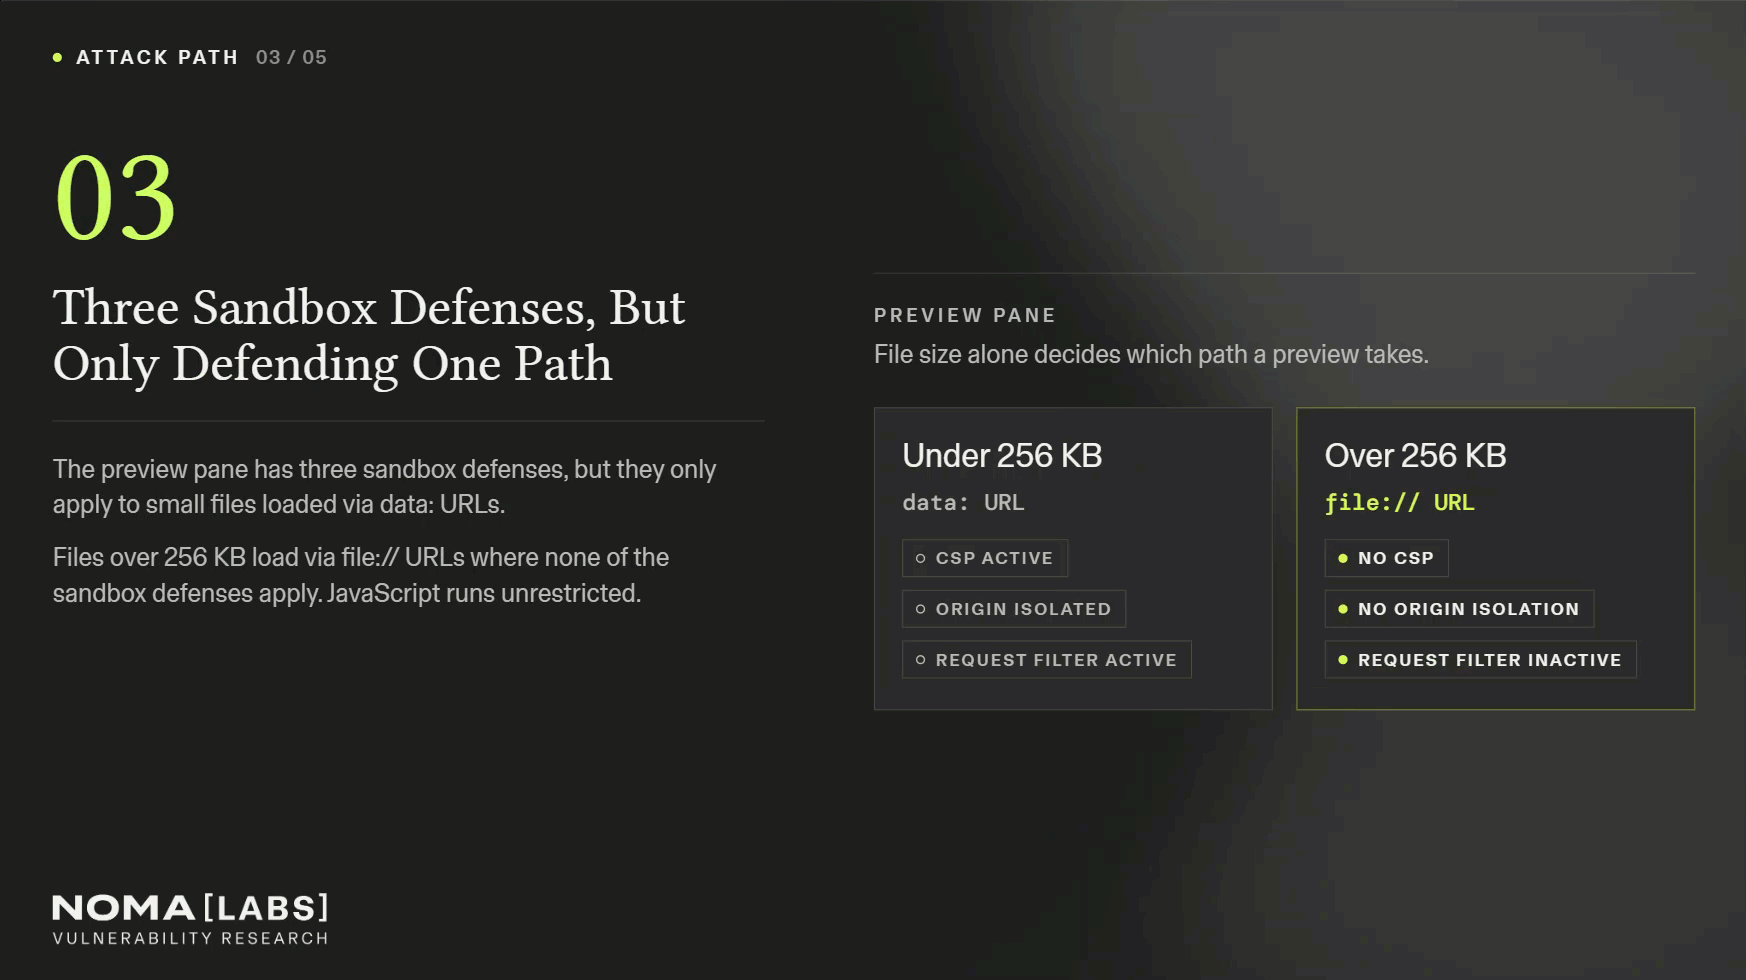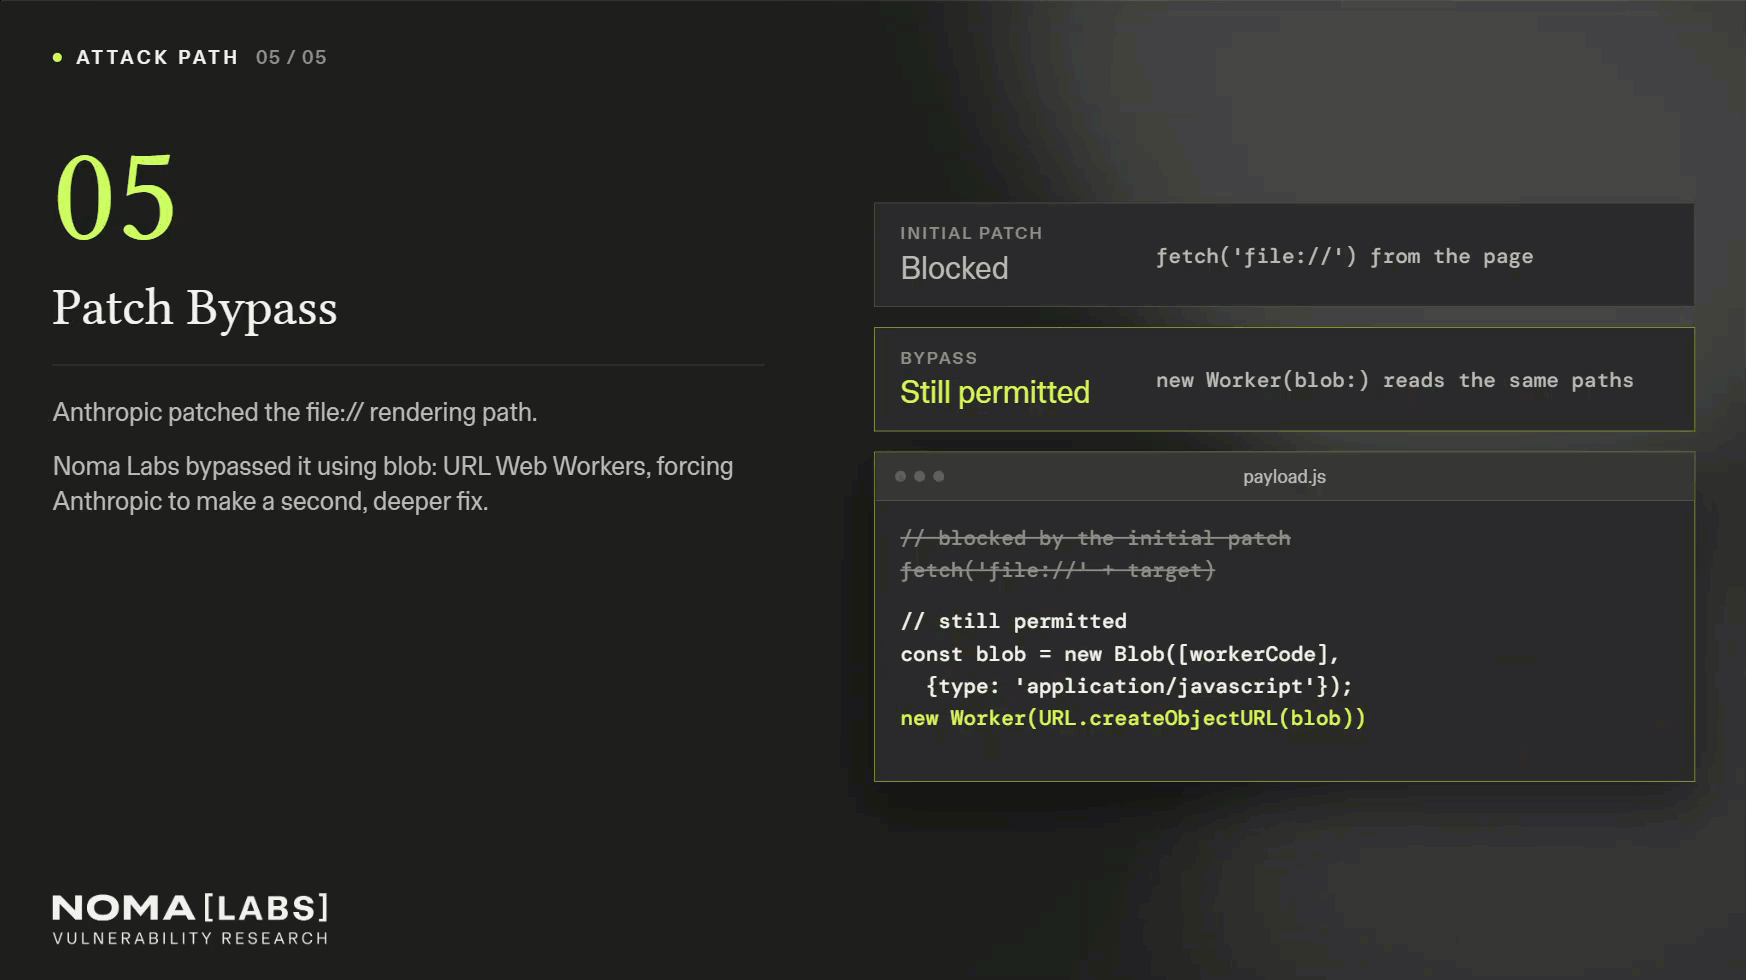
The preview pane is an Electron (Chromium) panel that renders HTML files Claude creates or edits. Noma's write-up describes three gaps that chained together:
- A size threshold. Files under 256KB were loaded as base64
data:URLs with a Content Security Policy that blocks scripts. Larger files were written to disk and loaded asfile://URLs, which skipped that policy. - The wrong origin. A
file://load gave the renderer access to the local filesystem instead of an isolated opaque origin. - An inactive filter. A request filter meant to block
file://access did not engage when static HTML was rendered from disk.
The lure was a public repository holding what looked like a coverage report, padded past 256KB and carrying JavaScript. The developer clones it and asks Claude to review the report. The preview renders it, the script derives the home directory from the temp file path, and reads files such as SSH keys, AWS credentials, npm and GitHub tokens, Kubernetes config, Docker auth and Git credentials. It sends them out with navigator.sendBeacon().
Source: Noma Labs
The three defenses, one by one
Noma describes the preview pane as having three layers between an HTML file and the machine. Understanding each shows why the chain worked.
- A Content Security Policy with
script-src 'none'. This tells the renderer to run no scripts at all from the page. It was applied to files loaded through thedata:path, and never reached thefile://path. - An opaque origin from
data:loading. A page loaded from adata:URL gets an origin that cannot fetch local files. A page loaded fromfile://does not have that isolation, and Noma notes that in Chromium it can read other local files throughfetch(). - A request filter on the dev server proxy. When the preview proxies a running dev server, such as a local React or Node app, the filter is active and blocks
file://reads. When the preview renders a static file straight from disk, such as a coverage report, Noma found that the filter does not engage, sofetch()calls resolve against the real filesystem.
None of the three is unusual design. The failure was that they were not tied to the same decision. The size check picked the loading path, the loading path picked the origin and the CSP, and the filter depended on a third condition, whether a dev server was involved. An attacker only needed one input, a file larger than 256KB, to land on the path where all three were off.
What the payload read and how it left
Noma's proof of concept was a repository that looked normal: source files, tests and a coverage report. Coverage reports often bundle source maps and CSS, so Noma notes a 500KB report raises no suspicion. The script derived the home directory from the temp file path, then pulled SSH private keys, AWS access keys and secrets, npm and GitHub auth tokens, Kubernetes cluster credentials, Docker registry auth, and Git identity and tokens.
The TL;DR also lists Claude's own OAuth tokens, and the victim's real IP address through WebRTC. The exfiltration used navigator.sendBeacon(), a web API that sends a one-way HTTP POST in the background. Noma explains why it worked: the Electron app has no CSP restricting outbound requests, and Electron runs its UI on a full Chromium engine with all the standard web APIs.
Anthropic scored the issue CVSS 8.7 (High) using CVSS v4.0 and, per Noma, treated the impact as equivalent to code execution on the host.
The key point, as CSO's coverage puts it: the script ran in the rendering process, not as an action by the AI agent. Controls aimed at the model did not cover this path.
The patch bypass
Anthropic triaged the report on July 9, 2026 and shipped an initial mitigation that blocked fetch() and XMLHttpRequest to file://. On July 24 Noma showed a bypass: the same file reads, made from a Web Worker created from a blob: URL. Anthropic confirmed the fix was incomplete in early August (Noma's write-up says August 3, its press release says August 5) and deployed the final fix on August 17, per Noma's press release.
What the Worker bypass looked like
Noma's write-up includes the bypass code. The first patch blocked fetch() and XMLHttpRequest calls to file:// from the main page context. The workaround created a Web Worker from a blob: URL. In Noma's words, the worker's fetch() originated "from a context that the CSP filter did not cover." The worker read the same sensitive files and posted the contents back to the main thread, which exfiltrated them with sendBeacon(). Noma states that all three original defects remained exploitable through this path.
The fix that shipped on August 17 covers the CSP, the file:// loading and the worker route together. Patching one fetch path at a time did not close the hole, because the hole was the loading path itself.
Disclosure timeline
Noma's timeline, as published on October 14, 2026:
| Date (2026) | Event |
|---|---|
| July 4 | Initial report to Anthropic with a full proof of concept |
| July 9 | Triage; Anthropic scores it CVSS 8.7 (High) |
| July 24 | Patch and retest; Noma reports the Web Worker bypass the same day |
| August 3 | Anthropic confirms the fix is incomplete and returns the report to triage |
| August 17 | Fix in Claude Desktop 1.30096.1 and later, delivered via auto-update |
| October | GitHub advisory and CVE listed as pending |
The gap between the first patch and the final one was about three weeks, and the public write-up came about two months after the last fix. For a reader, that means anyone on auto-update was protected long before the post appeared. Anyone who had turned off updates, or who runs a managed build that lags, was not.
Update (October 20, 2026): still no advisory or CVE in the public list
Noma's post and CSO's report on October 14 both said a GitHub Security Advisory and CVE were pending. When we reviewed the public security advisories page of the anthropics/claude-code repository on October 20, we did not see an entry that matches SneakPeek. We could not confirm a CVE ID either. The list does show a high-severity advisory from September 25 titled "Claude Desktop (macOS): opening a malicious file from a Cowork folder could run commands on the host", which is a separate issue and shows that desktop-app flaws are being tracked there. Until a SneakPeek advisory appears, treat Noma's August 17 fix date and version (1.30096.1) as the only official fix information in the sources reviewed, and check the advisory page again later.
What this means if you run AI coding agents
- Update. Confirm Claude Desktop is at 1.30096.1 or later. Auto-update should have done it, but check the version in the app.
- Treat repository files as untrusted input. Until you are sure you are patched, avoid previewing HTML from repositories you did not write. A report or demo page is code.
- Shrink what a script can reach. Remove long-lived credentials from developer machines and prefer scoped, short-lived tokens, as Noma and Sysdig advise in CSO's article.
- Watch the runtime layer. Agent-level logs may not show this activity. File reads of
~/.sshor~/.awsand unexpected outbound connections from the desktop app are the signals to look for. - Consider rotating SSH keys and cloud keys if you previewed untrusted HTML before the fix. No source reports exploitation in the wild, so this is precaution, not confirmation.
How to check where you stand
- Find the app version. Open the Claude Desktop app and look for its version in the app's about or settings screen. The fixed build is 1.30096.1 or later. The sources reviewed do not publish the affected range, so any older build is worth updating.
- Check that updates are on. The fix was delivered through auto-update. If your organization pins or delays desktop updates, confirm the pinned build is not older than the fix.
- Review recent clones. Large generated HTML files, such as coverage reports, in repositories you did not write are the lure Noma describes. You can list HTML files over 256KB in a checkout with
find . -name '*.html' -size +256k. A large file is not evidence of an attack, since real coverage reports are often large, but a large HTML file that contains inline<script>code and has no matching test tooling in the project deserves a look. - Look at the runtime layer. CSO quotes Sysdig's Crystal Morin saying agent-level logs would not necessarily capture this activity, and that file reads and outbound network connections are visible at the runtime layer instead. On a developer machine, that means endpoint monitoring or network logs, not the agent's own transcript.
If you did preview untrusted HTML before the fix and your machine held long-lived credentials, rotating them is a reasonable precaution. No source reviewed reports exploitation in the wild.
What the vendors and researchers recommend
Noma's Eli Ainhorn told CSO that organizations need to "keep AI coding tools updated, stop leaving long-lived credentials on developer machines, and use scoped, short-lived tokens where possible," adding that this alone "would have limited what this exploit could grab." Black Duck's Ronald Lewis, also quoted by CSO, argued that relying on size-based thresholds or client-side filters for a security boundary is fragile and that developer machines hold SSH keys, AWS credentials, Kubernetes configuration and OAuth session tokens.
Both points are practical. A script that runs inside a trusted app can read whatever your user account can read. The smaller that set is, the less a renderer bug is worth.
What Beam can and cannot do here
Beam's deny works on agent tool calls through Claude Code and Codex PreToolUse hooks. SneakPeek ran inside the preview renderer, so no tool call happened for a hook to judge, and Beam would not have blocked it. Beam is also not a kernel sandbox. What it does cover is the neighbouring path: if a poisoned repository instead steered the agent into reading credentials or running commands, Beam's hooks can flag or deny those actions, and redaction removes secrets before storage. For the monitoring concept, see what AI agent monitoring is.
Why it matters beyond one pane
An agent's tooling includes its viewers, not just its model. The same lesson appears in agentjacking through an MCP server and Cursor MCP config poisoning: content you did not write can reach a trusted process. A fixed bug does not change the habit worth keeping, which is reviewing what you open from unknown sources. The week's other Claude Code story, the plugin hash pin bypass, is a different bug in a different component, but it rests on the same assumption: that a control you configured is the control that ran.
For a broader view of how these incidents line up over the year, see the AI agent security incidents timeline.
Frequently asked questions
What is SneakPeek?
SneakPeek is a vulnerability in the Claude Code Desktop preview pane, disclosed by Noma Labs and scored CVSS 8.7 (High) by Anthropic. A malicious HTML file could run script with local file access when Claude previewed it.
Which version fixes SneakPeek?
Noma says the fix shipped in Claude Desktop 1.30096.1 and later through auto-update, with the final patch deployed on August 17, 2026. The affected version range was not published in the sources reviewed.
Did the attack need the user to approve anything?
According to Noma, no extra permission prompt appeared. The victim cloned a repository and asked Claude to look at a coverage report, and the preview rendered the file automatically.
Does it have a CVE?
Not at publication. CSO reports Anthropic is preparing a GitHub Security Advisory and has requested a CVE, and Noma lists the advisory as pending.
Was SneakPeek exploited in the wild?
None of the sources reviewed report exploitation in the wild. The research was reported to Anthropic on July 4, 2026 and fixed before public disclosure.
Would Beam have caught this?
Probably not. The script ran inside the preview renderer, not as a tool call by the agent, so hook-based checks on agent actions do not see it. Updating the app and limiting stored credentials are the effective defenses.
Related reading
Details are accurate as of October 14, 2026. A CVE and advisory were still pending; check Anthropic's advisory for later changes.